

1
/
из
5
OLYCOM
Managed L2+ Gigabit PoE Switch for Enterprise & Surveillance, 16 PoE + Dual SFP, 280W, PoE Watchdog
Managed L2+ Gigabit PoE Switch for Enterprise & Surveillance, 16 PoE + Dual SFP, 280W, PoE Watchdog
Обычная цена
$179.99 USD
Обычная цена
$189.99 USD
Цена со скидкой
$179.99 USD
Цена за единицу
/
за
Не удалось загрузить сведения о доступности самовывоза
Introduction
- The OM21816-PSE-GW occupies a specific and deliberate position in the product lineup: the managed counterpart to the OM21816-PSE-GE, sharing the same port architecture — 16 × Gigabit PoE, 2 × Gigabit RJ45 uplinks, 2 × Gigabit SFP uplinks — but adding the full L2+ managed feature stack that enterprise, surveillance, and telecom deployments require when DIP switch simplicity is no longer sufficient for the network's traffic segmentation, security, and operational visibility demands.
- The PoE capability leads with a meaningful upgrade: 280W total budget — 40% more than the unmanaged variant — with intelligent per-port power allocation, PoE Watchdog for automatic device recovery, PoE scheduling for time-based port power control, and per-port temperature monitoring that reports thermal conditions at the switch level before heat-related failures occur.
- These are not checkbox features; in a surveillance or enterprise deployment where dozens of PoE endpoints must stay online continuously, automatic device reboot, scheduled power cycling of off-hours equipment, and proactive thermal alerts directly reduce the operational labor cost of keeping the network running.
- On the switching side, 40Gbps non-blocking capacity, 29.76Mpps forwarding rate, and 4Mbit buffer memory back a feature set that spans from basic VLAN and STP through IPv4/IPv6 static routing, DHCP server/relay, 802.1X with RADIUS/TACACS+, Dynamic ARP Inspection, IP Source Guard, DSCP/802.1p QoS with 8 queues per port, and full SNMP v1/v2c/v3 / Web GUI / SSH v2 / Telnet management — making the OM21816-PSE-GW capable of serving as the distribution-layer switch in a medium-sized network, not merely an access-layer device.
- With 6KV common-mode surge protection, ±8KV ESD immunity, CE / FCC / RoHS certification, and a standard 440mm 1U rack form factor, it integrates into enterprise wiring closets, telecom equipment rooms, and surveillance control centers as a production-grade infrastructure component rated for continuous 24/7 operation.
Key Features
- 16 × Gigabit PoE + 2 × Gigabit RJ45 + 2 × Gigabit SFP — Full Hybrid Uplink Architecture — Gigabit speed on every port; all four uplink ports simultaneously active for LACP aggregation, active/standby failover, or split copper-fiber traffic routing; 8K MAC address table; 10KB jumbo frame support for HD video and high-volume data transfers
- 280W Total PoE / 30W Per Port with Intelligent Management:
- IEEE 802.3af (15.4W) and 802.3at (30W) auto-sensing on all 16 PoE ports
- PoE Watchdog — monitors each powered port for device hang conditions; automatically cycles port power to recover a frozen camera, AP, or phone without manual intervention or a field visit
- PoE Scheduling — time-based port power control; power down non-critical endpoints during off-hours; reduce energy consumption and extend PoE hardware lifespan across devices that do not require 24/7 power
- Per-Port Temperature Monitoring — reports thermal conditions at individual port level through SNMP and Web GUI; enables proactive intervention before heat-related PoE circuit degradation occurs in high-ambient-temperature wiring closets
- 40Gbps Switching / 29.76Mpps Forwarding / 4Mbit Buffer — Non-blocking wire-speed performance across all 20 ports simultaneously; 128MB DDR SDRAM and 16MB flash for reliable configuration storage and switch OS operation; forwarding delay suitable for latency-sensitive VoIP and real-time video traffic
- VLAN — Full Enterprise Segmentation:
- 802.1Q Tag VLAN with Access / Trunk / Hybrid port modes; VLAN ID range 1–4094; up to 256 active VLANs
- Voice VLAN — automatic identification and prioritization of VoIP traffic; IP phones receive QoS treatment without per-port manual configuration
- MAC VLAN — VLAN assignment based on source MAC address regardless of physical port
- Surveillance VLAN — dedicated VLAN for IP camera traffic isolation; prevents surveillance traffic from competing with user data on shared uplinks
- Spanning Tree — Loop Protection at Every Layer:
- STP / RSTP / MSTP; BPDU Guard and BPDU Filter on edge ports; Root Guard on designated ports; prevents accidental topology changes from misconfigured downstream devices
- Loopback Detection for per-port loop identification without STP; Storm Control for broadcast, multicast, and unknown unicast suppression
- IPv4/IPv6 Static Routing + Layer 3 Functions — Inter-VLAN routing without a separate router for small-to-medium network deployments; DHCP Server, DHCP Relay, and DHCP Snooping with Option 82; ARP and Neighbor Discovery; IP Source Guard binds IP-MAC-port for anti-spoofing at the access layer
- Security — Defense in Depth:
- 802.1X port and MAC authentication with RADIUS and TACACS+ AAA backend
- Dynamic ARP Inspection prevents ARP spoofing and man-in-the-middle attacks
- DoS attack protection; Port Isolation; MAC address filtering; static and dynamic MAC learning control
- SSHv2 and HTTPS for encrypted management sessions; Telnet and HTTP disabled by policy when security posture requires
- QoS — Eight Queues Per Port:
- 802.1p CoS and DSCP classification; WRR and SP scheduling; per-port ingress and egress bandwidth control; rate limiting at granular step sizes
- Ensures VoIP calls, video conferencing streams, and surveillance feeds receive deterministic forwarding priority over bulk data transfers on shared uplinks
- LACP Link Aggregation — Dynamic 802.3ad LACP and static link aggregation; bond dual RJ45 or dual SFP uplinks for doubled throughput or active/standby failover; essential for distribution-layer connections where uplink redundancy is a network design requirement
- Management & Diagnostics:
- Web GUI, CLI, Telnet, SSHv2, SNMP v1/v2c/v3, RMON for comprehensive operational visibility
- LLDP / LLDP-MED for automatic topology discovery and IP phone / AP identification
- System logs, Ping, Traceroute, Copper Cable Test (TDR) for fault isolation without external test equipment
- SNTP time synchronization; firmware upgrade via Web GUI or TFTP
- 6KV Common-Mode / 2KV Differential Surge Protection / ±8KV ESD — Full port-level transient protection on all copper interfaces
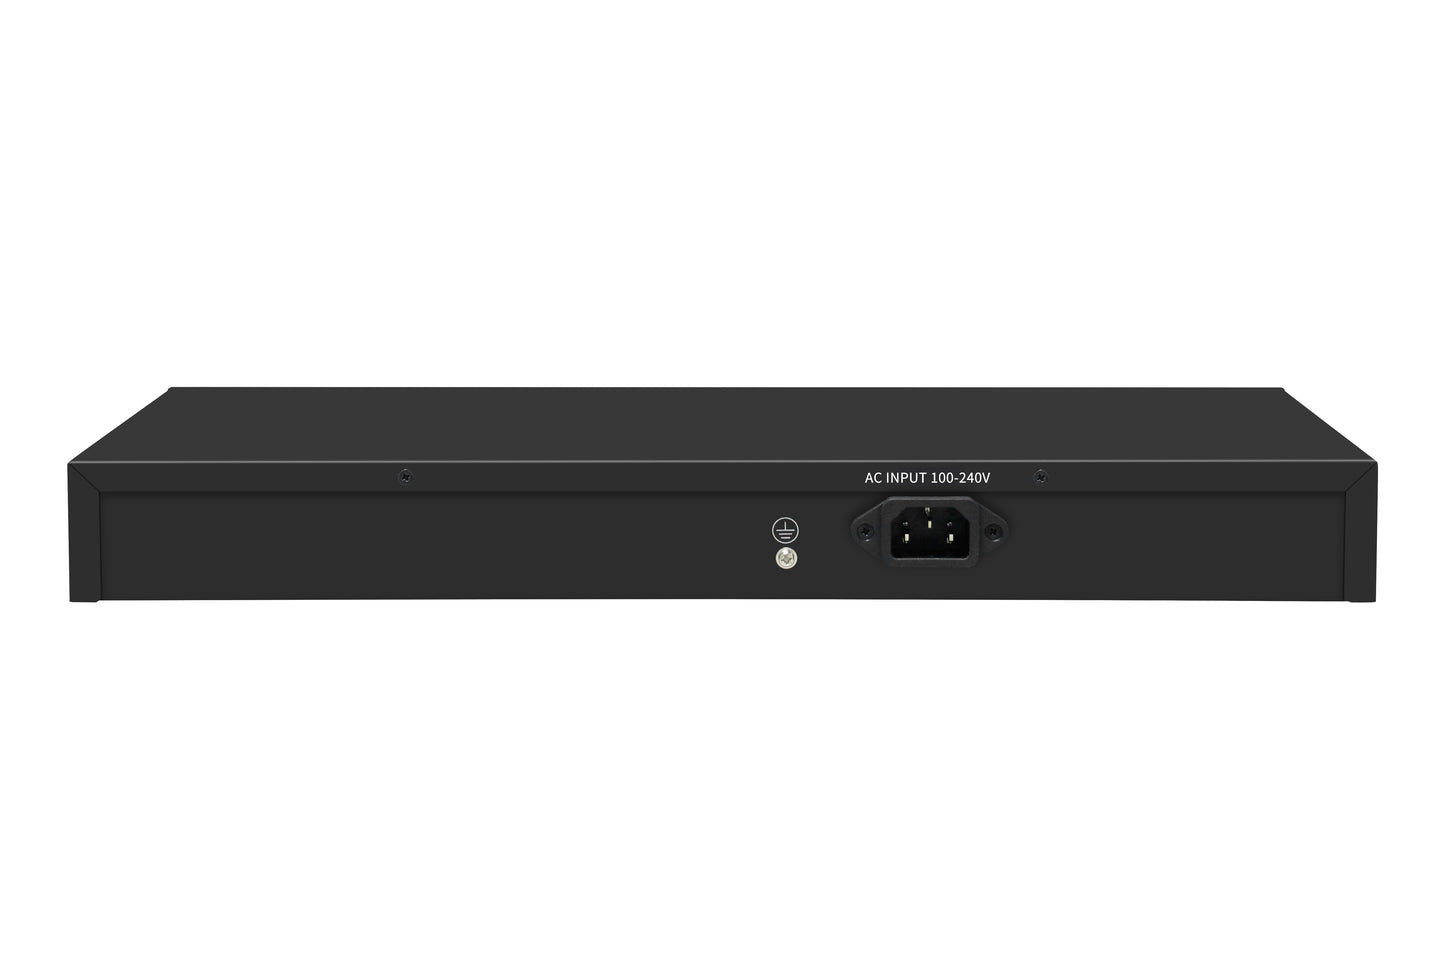
- AC 100–240V / 52V output (3.84A or 5.76A PSU options) / 440 × 204 × 44mm 1U / CE / FCC / RoHS
Applications
- Enterprise Campus Distribution & Access Layer — In medium-sized enterprise networks where the distribution switch must perform inter-VLAN routing, enforce 802.1X authentication, and provide PoE to the access layer simultaneously, the OM21816-PSE-GW eliminates the need for a separate router or L3 switch at each IDF. Voice VLAN automatically handles IP phone QoS; Surveillance VLAN isolates camera traffic from user data; LACP bonds the fiber SFP uplinks to the core for redundant high-throughput backbone connectivity; DHCP server handles access-layer IP assignment without a central server dependency at each distribution point. The result is a single managed device that handles routing, switching, security, and PoE delivery for an entire floor or building wing
- Large-Scale IP Surveillance & Smart City Infrastructure — Surveillance networks at scale — city-wide CCTV deployments, campus security systems, industrial facility monitoring — require more than PoE delivery: they require per-camera VLAN isolation to prevent lateral movement between compromised cameras, PoE Watchdog to automatically recover frozen devices without field visits, QoS prioritization to ensure camera streams are not disrupted by competing traffic, and SNMP visibility for centralized fault monitoring across hundreds of switch nodes. The OM21816-PSE-GW provides all four in a single managed platform, with the 280W PoE budget supporting 30W PTZ cameras and IR-illuminated dome cameras that draw more than standard 802.3af devices
- Telecom & ISP FTTB/FTTH In-Building Aggregation — Fiber-to-the-building deployments use the OM21816-PSE-GW as the subscriber-side L2+ aggregation switch: dual SFP uplinks connect to the building's fiber handoff; per-subscriber VLAN assignment via 802.1Q Trunk ports enforces traffic isolation between tenants; IP Source Guard and Dynamic ARP Inspection prevent subscriber spoofing and ARP poisoning attacks that are endemic in shared-infrastructure multi-tenant environments; DHCP Snooping with Option 82 passes subscriber circuit identification to upstream RADIUS and provisioning systems; SNMP v3 provides encrypted per-device monitoring from the ISP's NMS platform. The PoE capacity simultaneously powers building Wi-Fi APs, IP intercoms, and CPE devices from the same switch
- Government & Public Sector Critical Networks — Government facilities, public safety communications centers, and municipal smart infrastructure require the combination of security depth, management visibility, and operational resilience that the OM21816-PSE-GW provides. TACACS+ integration enforces individual administrator accountability for configuration changes; SSHv2 and HTTPS encrypt all management sessions; DoS protection defends the switch's control plane against deliberate attack; MSTP with BPDU Guard prevents accidental topology disruption from unauthorized downstream device connections; and the RMON capability provides the historical traffic data that compliance audit requirements demand. The PoE Scheduling feature adds the energy management capability increasingly required in public sector procurement specifications
- Education Networks — Security, Scale & Operational Efficiency — University and school networks face the specific challenge of managing high-density student device access while maintaining security separation between student, staff, faculty, and surveillance VLANs — and doing so with limited IT staff across multiple buildings. The OM21816-PSE-GW's LLDP-MED automatically identifies and correctly provisions IP phones and APs as they are connected; Voice VLAN handles phone QoS without per-port configuration; 802.1X with RADIUS enforces per-user authentication against the institution's directory; PoE Scheduling powers down student-facing APs outside teaching hours; and the Web GUI provides the graphical management interface that campus network staff with limited CLI experience can operate effectively across a multi-building deployment
Делиться